Compliance Without the Chaos: How Comper Makes EU CRA Readiness Automatic
The EU Cyber Resilience Act (CRA) is officially active, and for software and product teams, it presents a daunting operational challenge. Mandated 24-hour early warnings on the Single Reporting Platform (SRP) for actively exploited vulnerabilities, mandatory technical documentation, and continuous software supply chain tracking threaten to impose a massive friction tax on engineering velocity. But regulatory compliance shouldn't mean freezing sprint cycles to manually audit dependencies or draft static architectural diagrams.
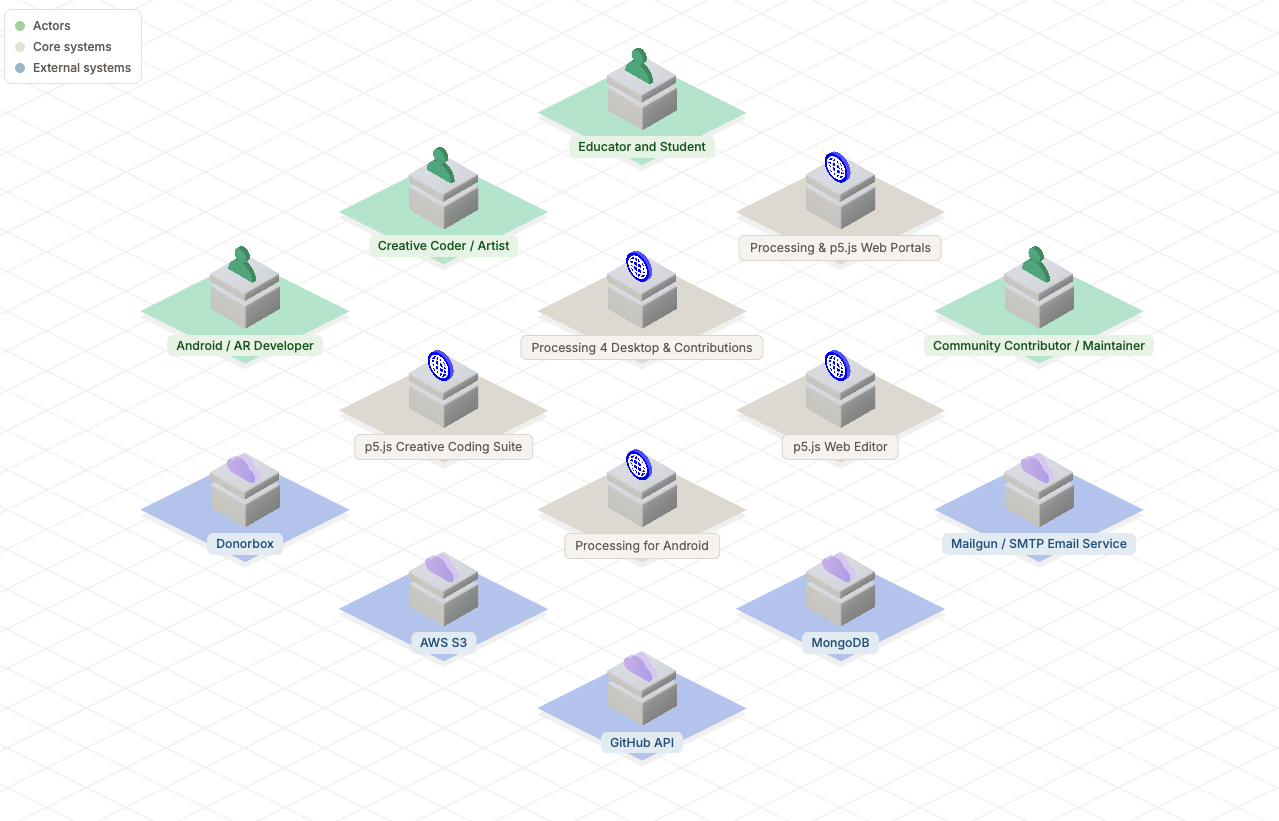
Automated Documentation and Zero-Friction Visibility
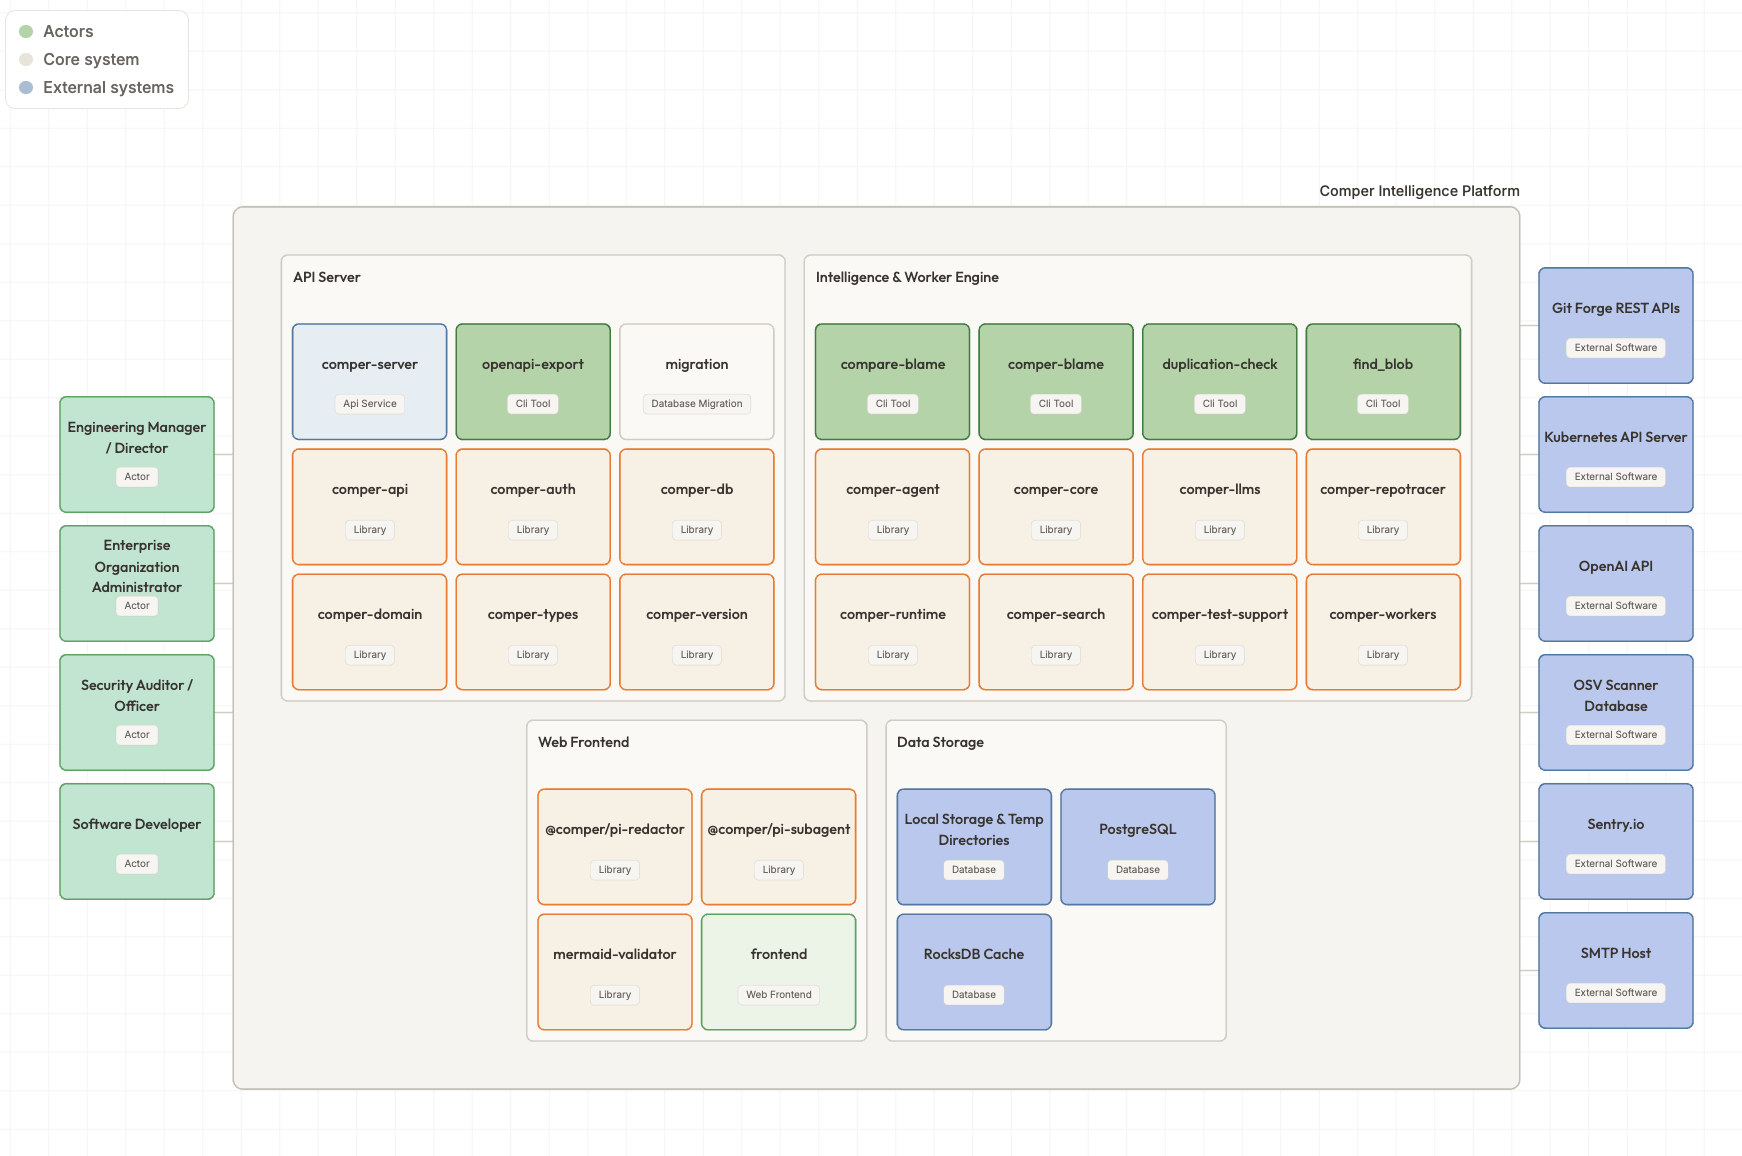
Most compliance failures occur because developer documentation is static, rotting away in abandoned wikis while source code moves forward every hour. Comper flips this dynamic by turning your code repositories into a continuous, self-updating single source of truth. As your engineers write, refactor, and commit code, Comper automatically extracts system structures to generate living architecture diagrams. Your codebase remains fully documented and CRA-compliant by default, eliminating manual developer overhead.
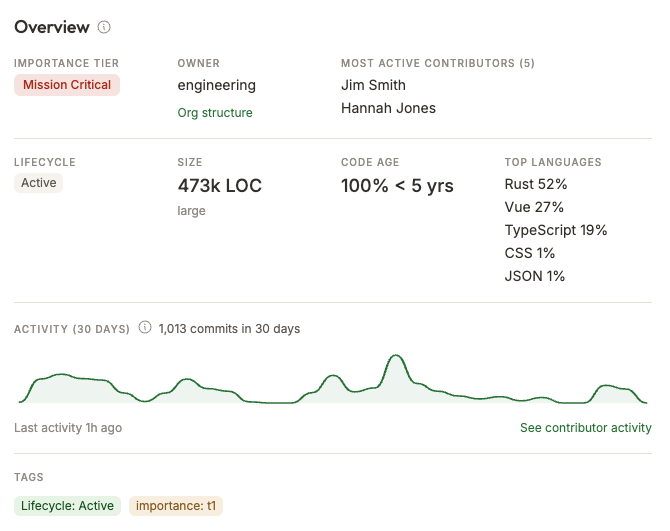
Find the Critical People - Beat the 24-Hour SRP Clock with Real-Time Context
When an actively exploited flaw surfaces in production, the CRA’s strict 24-hour SRP early warning deadline starts ticking immediately. The primary delay in incident response isn't writing a patch, it's identifying which team owns the affected component, tracing nested dependencies, and assessing downstream impact. Comper provides real-time security intelligence that instantly maps code ownership, component dependencies, and bus-factor risks. This empowers you to time save critical time in finding the write owners of the code.
Additionally security leads get instant blast-radius assessments to triage vulnerabilities, notify key maintainers, and submit required SRP notifications well before the deadline passes.
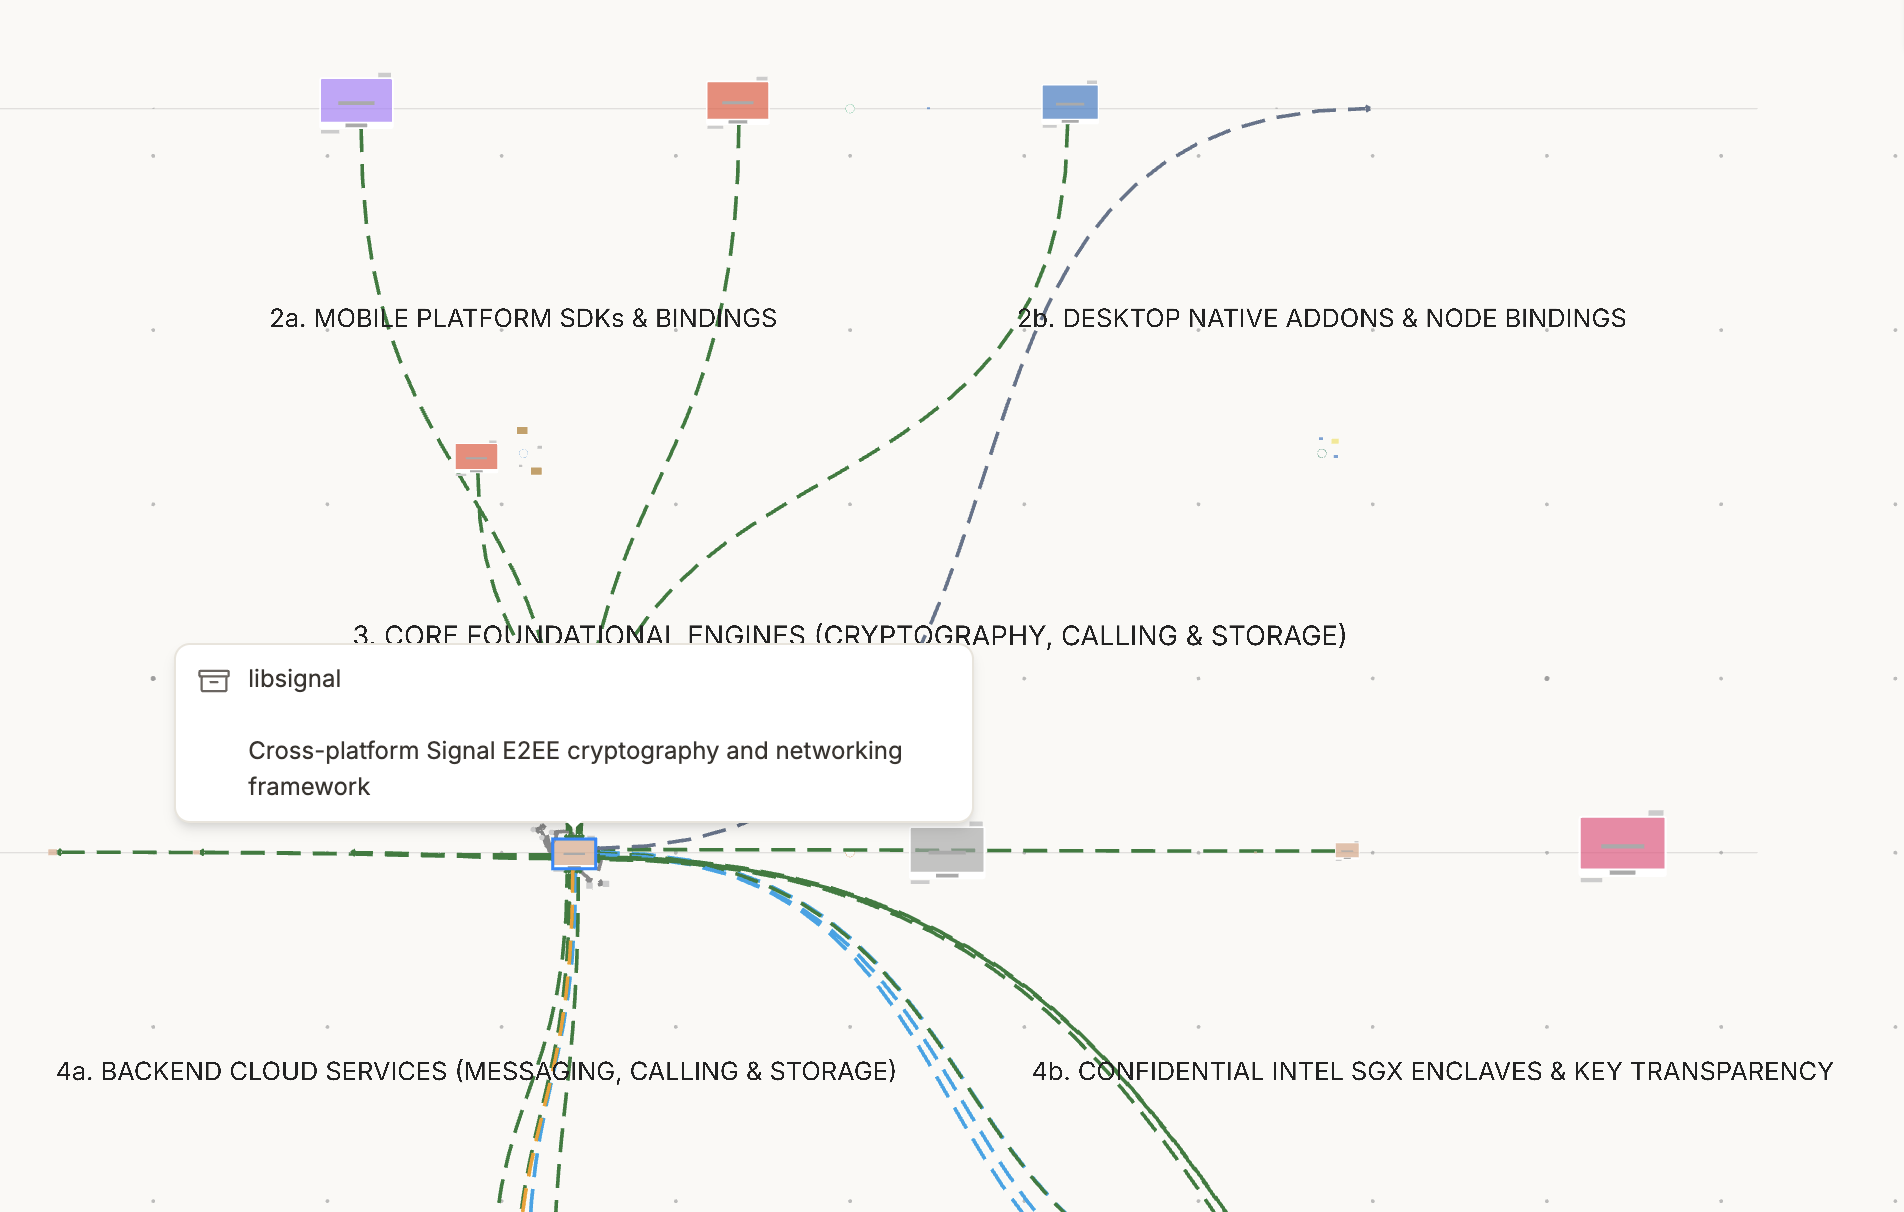
Complete Supply Chain Due Diligence
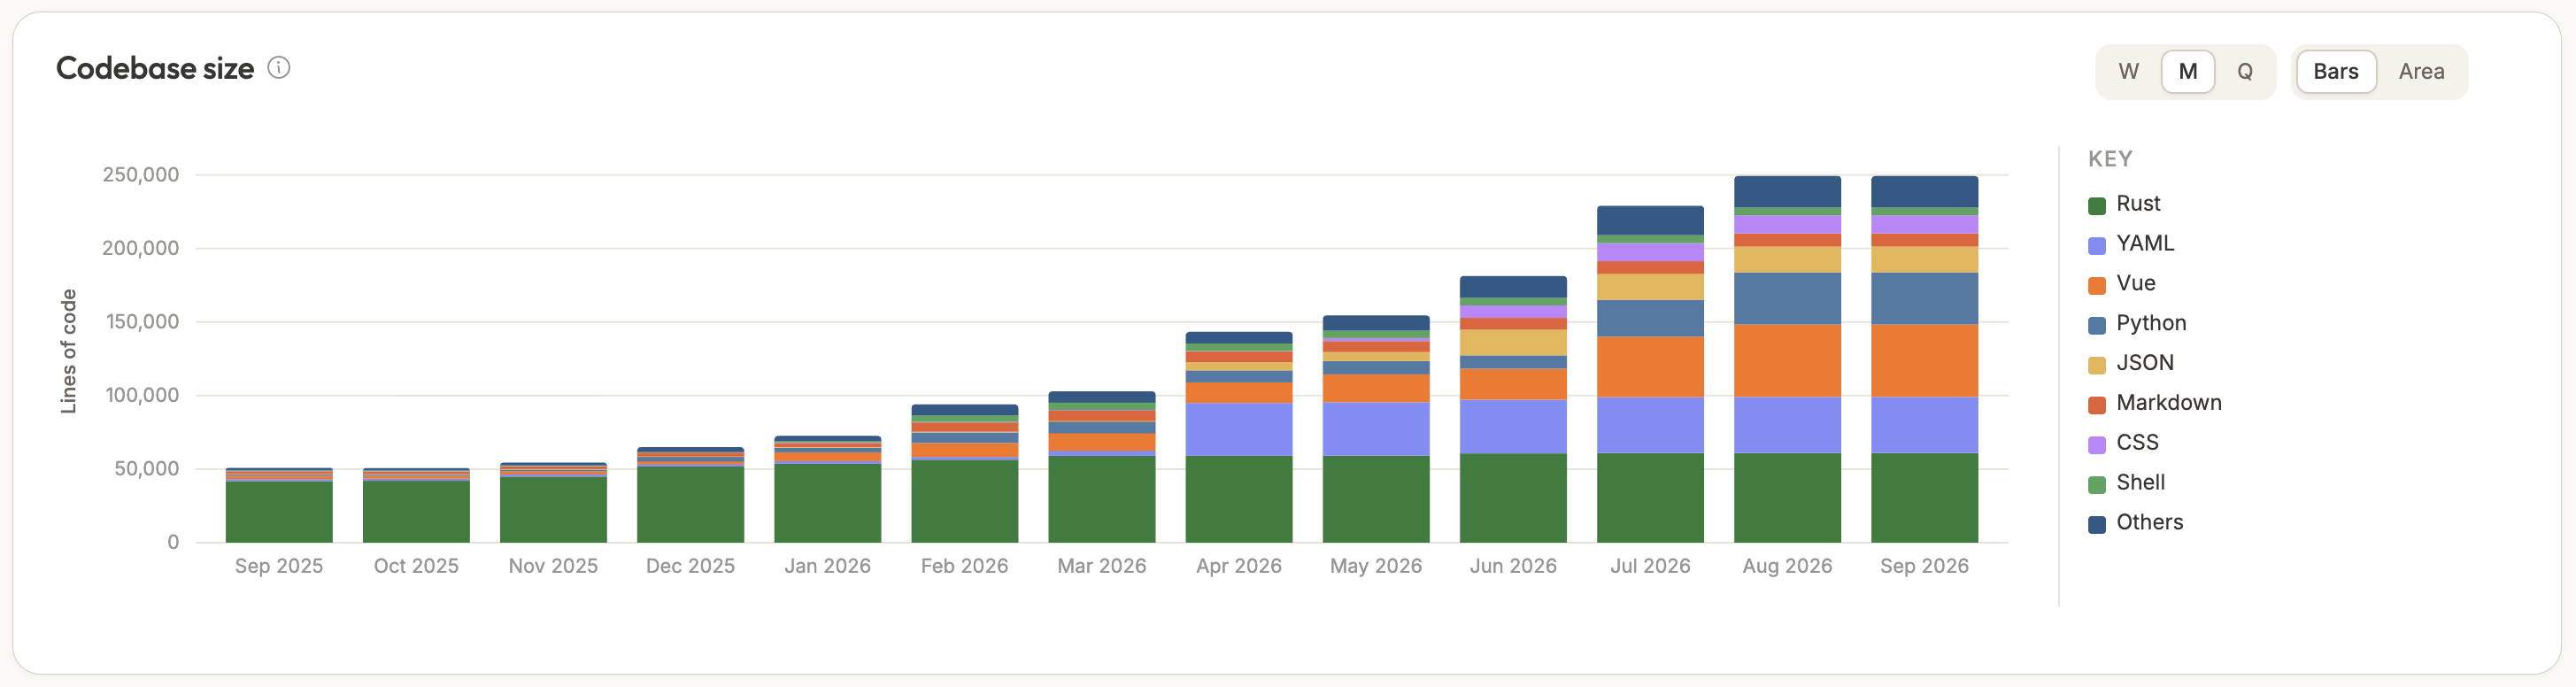
Open-source components and third-party libraries now require rigorous due diligence under CRA rules. Comper exposes hidden code bloat and deep transitive dependencies across multi-language repositories, giving compliance leads complete, real-time visibility into your entire software supply chain.
Compliance doesn't have to be a bureaucratic nightmare that halts product development. By combining automated architectural documentation, real-time dependency visibility, and instant vulnerability context, Comper transforms CRA readiness from a manual burden into an invisible background process. You keep building and shipping features; Comper keeps your software compliant and secure.